Facebook Vulnerability Allows Attackers to Prevent Anyone From Blocking Them
Hello,
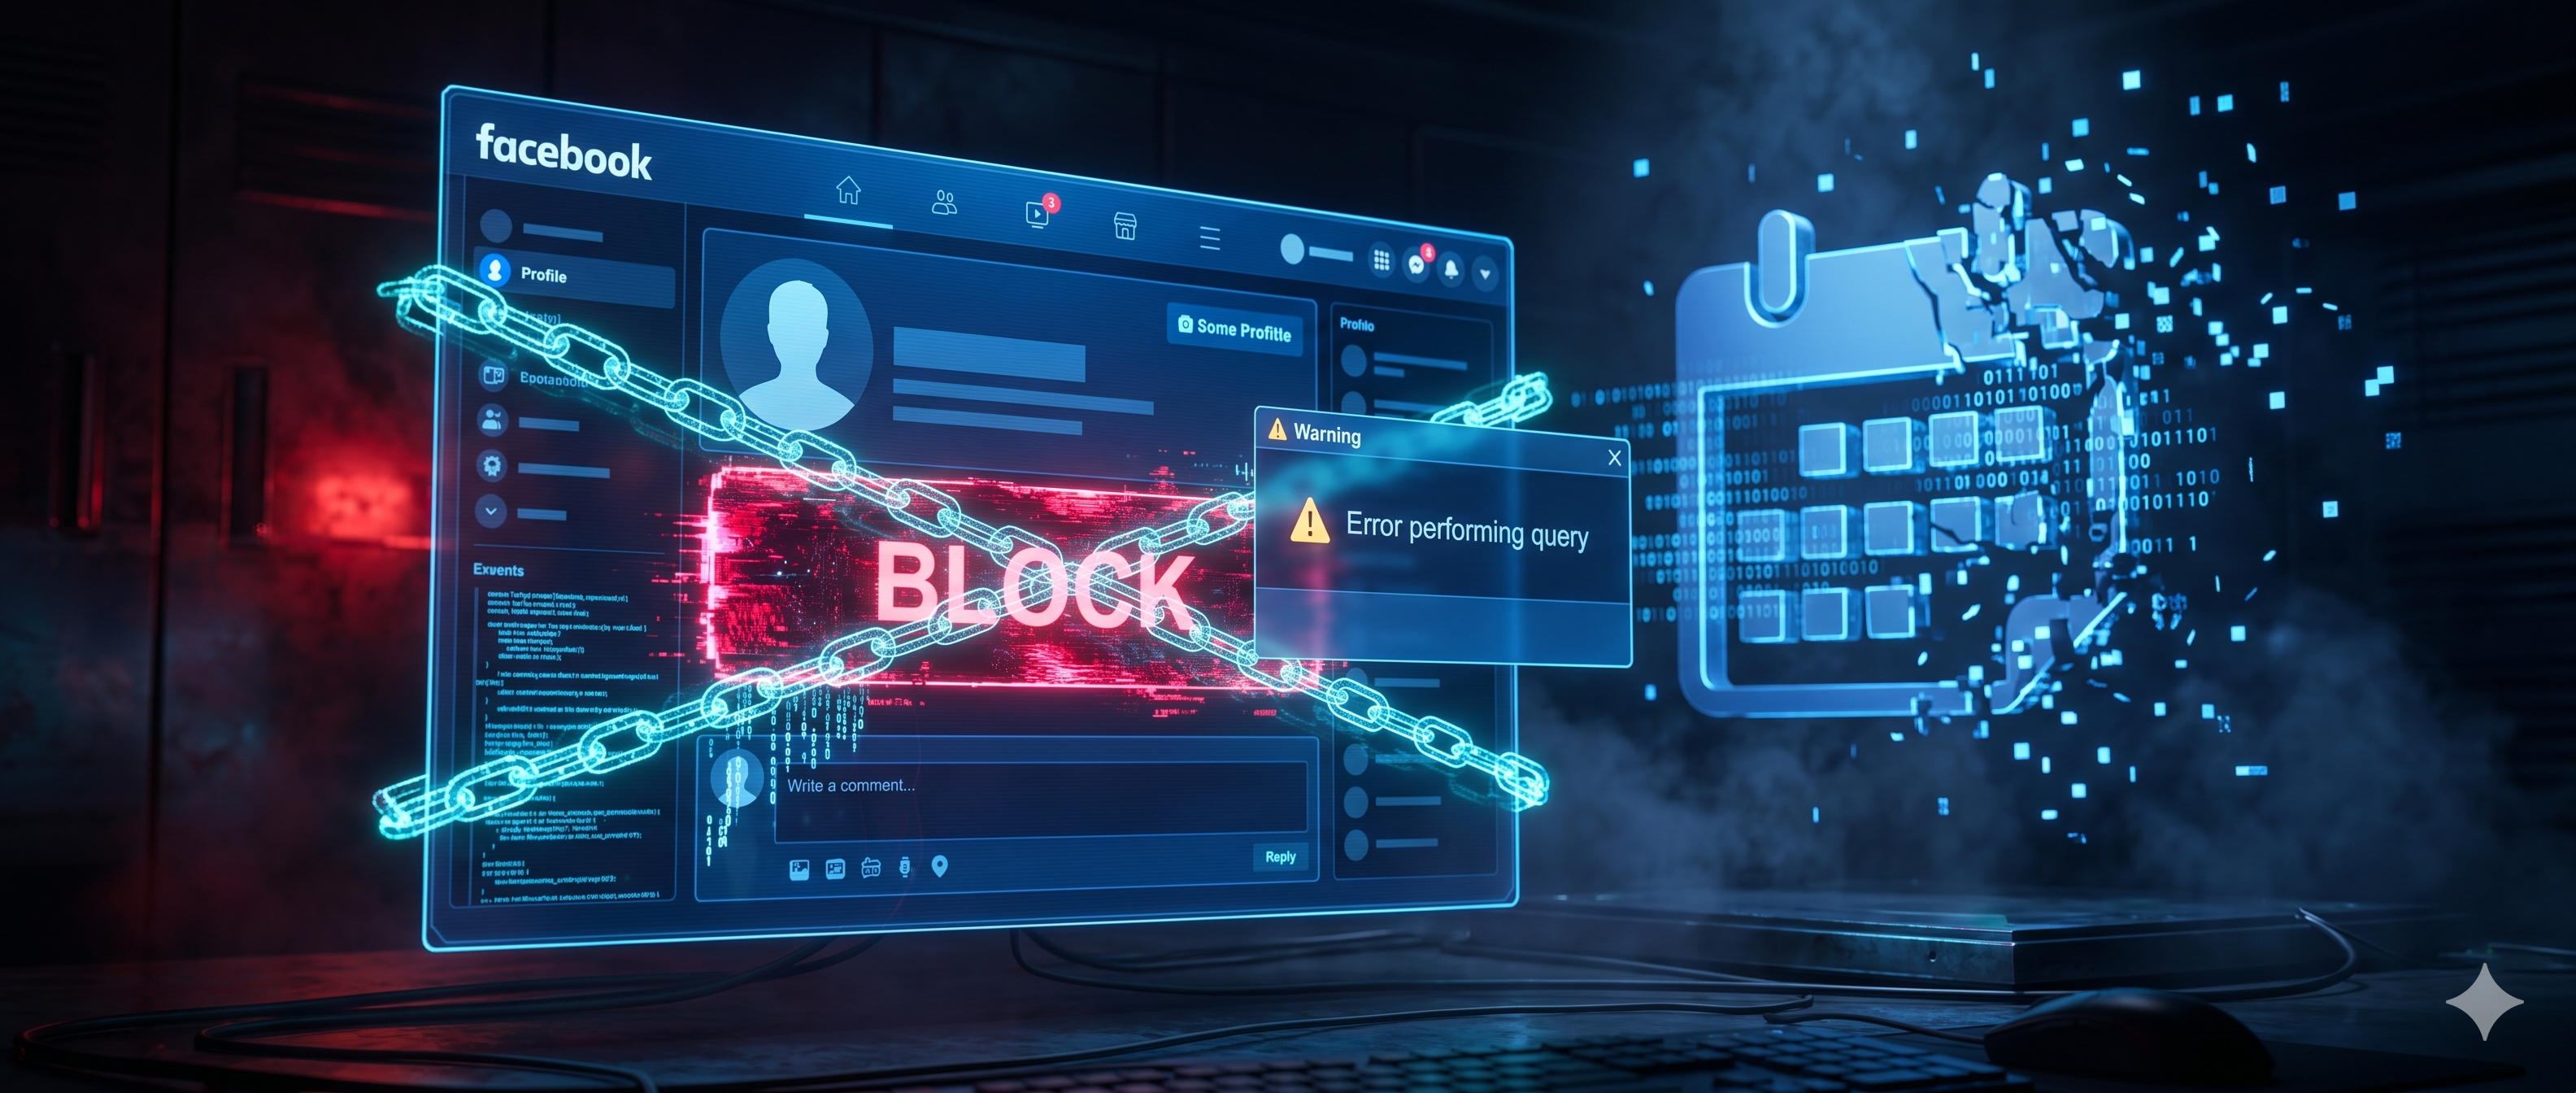
Today, I'm sharing a unique logical vulnerability I discovered in Meta's bug bounty program. This flaw allows an attacker to completely manipulate Facebook's privacy logic and permanently prevent any user from blocking them.
📝 Description of Vulnerability
- Recurring Events: On Facebook Events, a user can navigate to
https://www.facebook.com/events/create/and create a recurring event—which is simply a single event that repeats at different time intervals. - The Logic Flaw: If you create a recurring event and then immediately delete it, the account enters a glitched state. Any Facebook user who tries to block you after this will encounter a system error that prevents the block from finalizing.
🎯 Exploitation Scenario
- The Intent: The attacker wants to permanently prevent any Facebook user from blocking them.
- The Setup: The attacker goes to the events creation page, clicks “Repeat event”, sets it to repeat twice, and clicks “Create event”.
- The Trigger: The attacker deletes this recurring event to trigger the account glitch.
- The Abuse: The attacker posts abusive comments on a victim’s posts or interacts with them inappropriately.
- The Failure: The victims try to block the attacker but fail completely, encountering the error message:
"Error performing query."
💥 Impact of the Vulnerability
- Total Block Failure: The victim is completely unable to block or restrict the attacker’s Facebook account.
- Continuous Harassment: Offensive comments remain visible to the victim and to all other users, enabling unrestricted cyberbullying.
- Infinite Loop: The victim is forced to manually delete offensive comments, but the attacker can immediately post new ones without limitation.
- User Confusion: The victim has no clear indication or explanation as to why blocking is failing, leaving them feeling exposed and unsafe.
- Safety Undermined: This vulnerability enables attackers to bypass Facebook’s fundamental safety control (blocking), directly undermining user protection.
🛠️ Steps to Reproduce
From Attacker’s Side:
- Targets a victim and decides to permanently disable their ability to block the attacker on Facebook and Messenger.
- Navigates to
https://www.facebook.com/events/create/. - Clicks “Repeat event”, sets it to repeat twice, and clicks “Create event”.
- Deletes the newly created recurring event.
- Goes to the victim's profile and posts offensive comments.
From Victim’s Side:
- Opens the post, notices the abuse, and attempts to block the attacker’s account.
- Result: The blocking action fails, and the system displays the error:
"Error performing query."
🎥 Proof of Concept Video
🎥 Proof of Concept Video
For a detailed, step-by-step demonstration of the full exploit chain, watch the Official POC Video on Google Drive 🚀.
📅 Bug Bounty Timeline
- October 6, 2025: Reported to Meta Bug Bounty.
- October 7, 2025: Triaged by the security team.
- October 8, 2025: Fix deployed to production.
- November 3, 2025: Bounty awarded by Meta! 🎉
👤 Follow Me:
About the author
- AI Red Teamer & Bug Bounty Hunter | BSc in Computer Science | Recognized by: Google, Facebook, GitHub, Yandex, Quora, Oppo, Yelp, Teleport
Comments
Join the discussionNo comments yet. Be the first to comment.