Teleport Critical Privilege Escalation Vulnerability ($21,000 Bounty)
Hello,
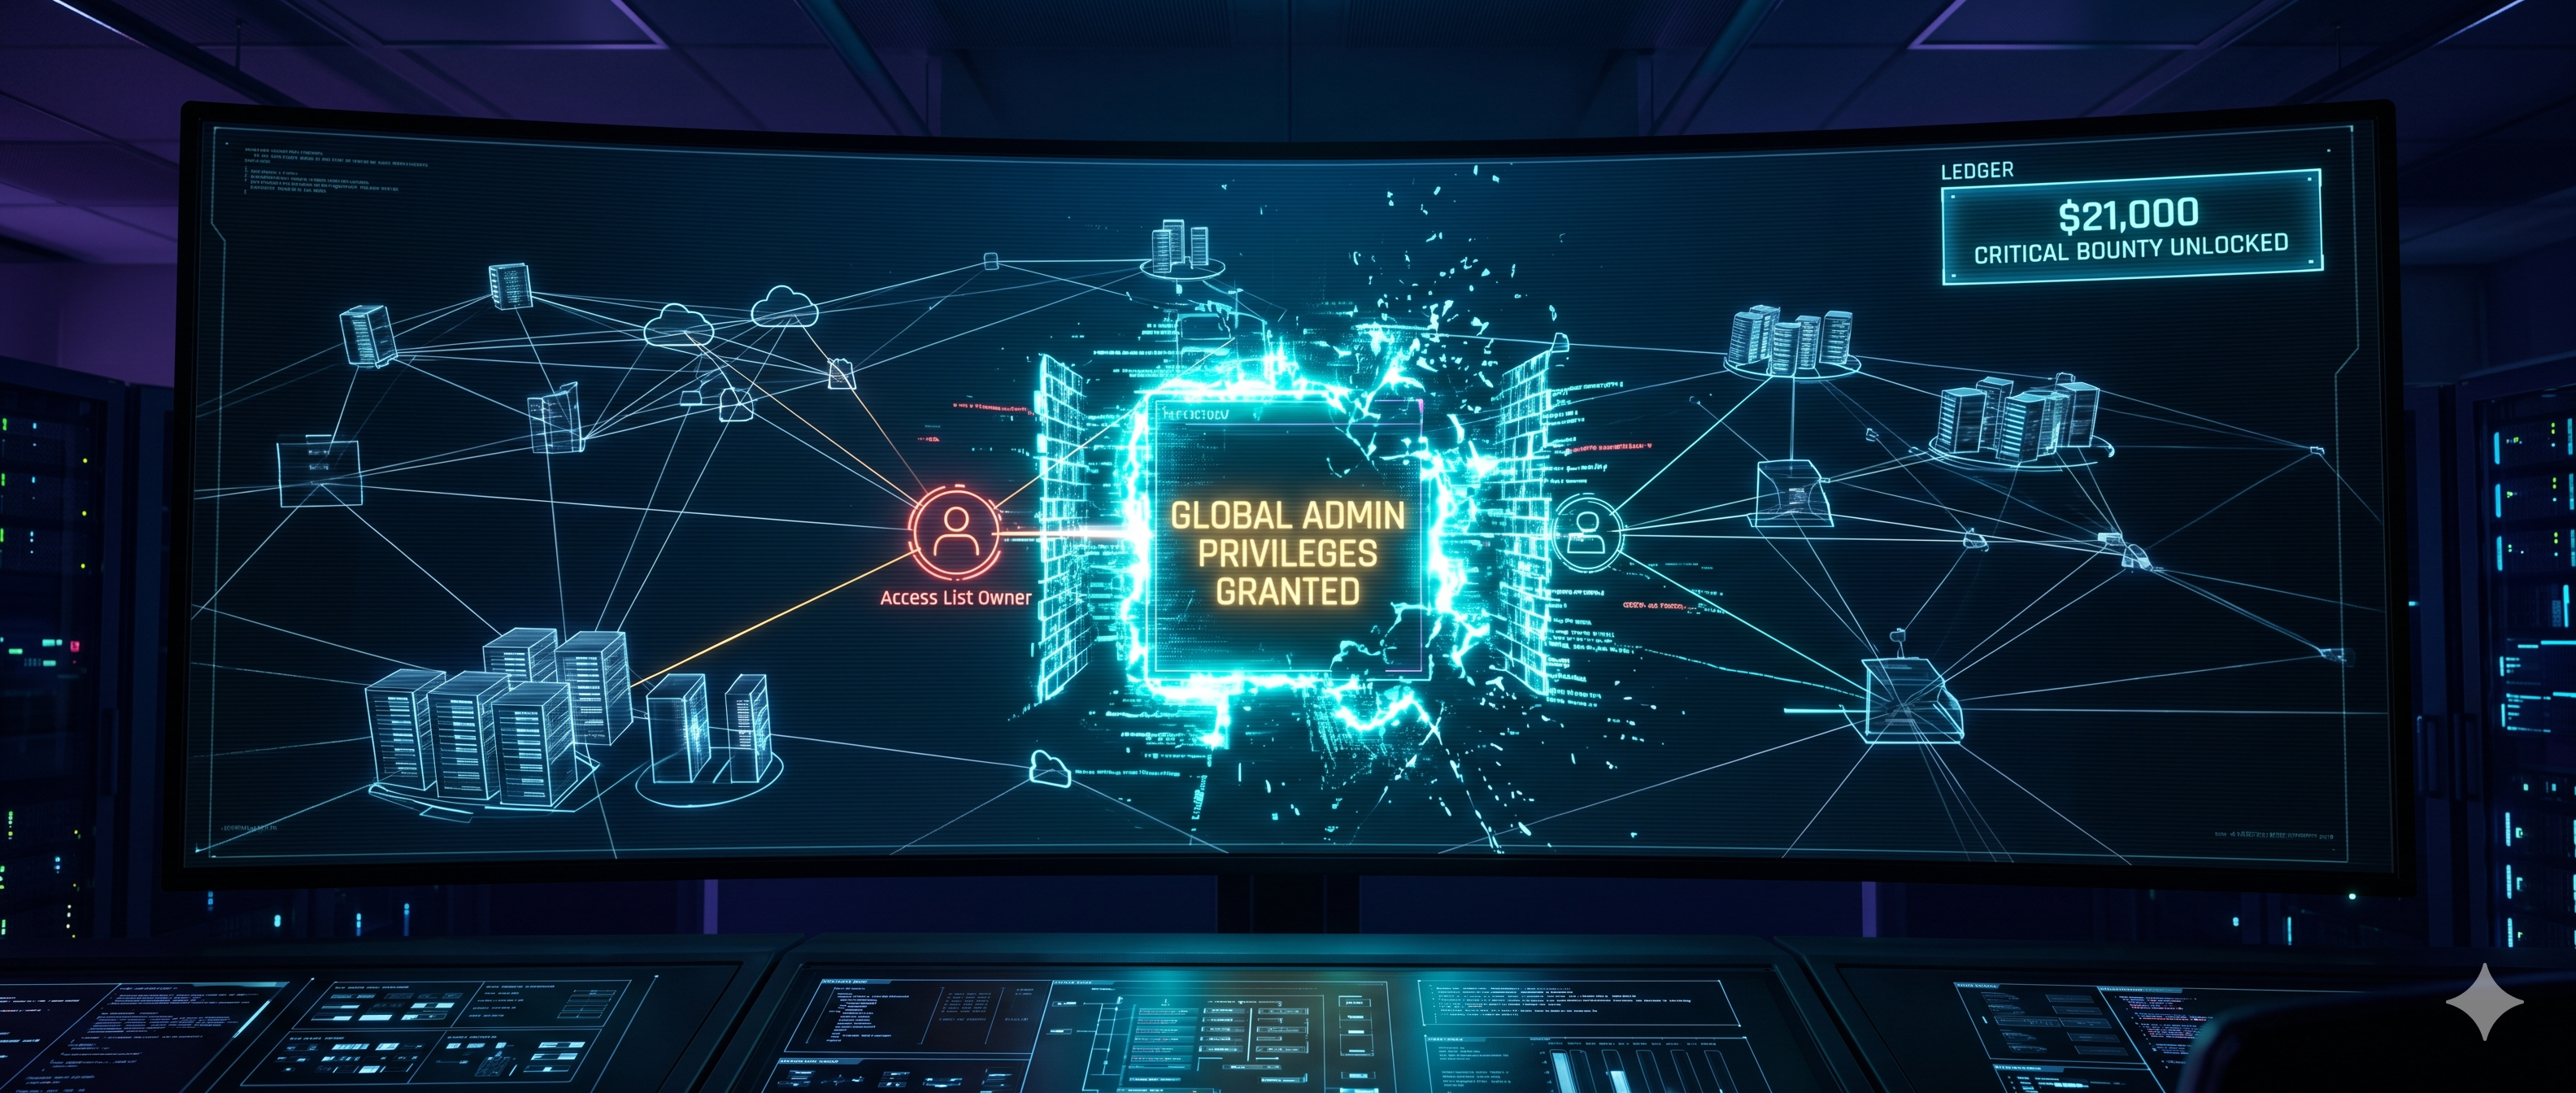
Today, I'm sharing a critical vulnerability I discovered in Teleport's bug bounty program. This privilege escalation flaw allows an Access List Owner to bypass access control policies and systematically elevate their account's role to Admin, gaining full control over the organization.
📝 Summary
Go to
[your-domain.teleport.sh/web/accesslists]. Create a new access list and add a role to "Roles Granted," e.g.,"reviewer"role. Add a user as the Access List Owner. The user, as the Access List Owner, can escalate the role of the list to higher roles, thereby escalating their own account's role. This is a prohibited procedure, as stated in the official documentation, that Owners are not able to control what roles and traits are granted by the Access List.
🛠️ Steps To Reproduce
1️⃣ From Organization Owner Account:
- Go to
[your-domain.teleport.sh/web/accesslists]. - Create a new access list.
- Add a user as List Owner.
- Add a role to "Roles Granted," e.g.,
"reviewer"role.
2️⃣ From Access List Owner Account:
- Add a new member to the access list and intercept the request.
- Add
"editor"role on"grants roles". - The
"editor"role will be added to "Permissions Granted". - Logout and re-login to the account.
- Result: Now, the user has the
"editor"role and can perform any action on the entire organization.
🎥 Proof of Concept Video
🎥 Proof of Concept Video
For a detailed, step-by-step demonstration of the full exploit chain, watch the Official POC Video on Google Drive 🚀.
💥 Impact
- Privilege Escalation: Direct violation of the principle of least privilege.
- Unauthorized Access: High potential for unauthorized access to highly sensitive information.
- Security Breach: Risk of totally compromising the overall security of the system.
- Violation of Access Control Policies: Complete contradiction with Teleport's official documentation and security policies.
- Risk of Insider Threats: Potential exploitation by malicious insiders with limited access.
📅 Bug Bounty Timeline & Updates
| Date (UTC) | Action / Activity | Status / Reward |
|---|---|---|
| Dec 11, 2023, 11:09pm | ⚠️ Severity Updated | Changed from Critical to Medium (6.1) |
| Dec 11, 2023, 11:41pm | 🚨 Severity Escalated | Changed from Medium (6.1) back to Critical (9.0) |
| Dec 11, 2023, 11:59pm | 🎯 Status Changed | Triaged (See team comment below) |
| Dec 12, 2023, 9:33pm | 💰 Bounty Rewarded | $20,000 Bounty Paid 🎉 |
| Dec 20, 2023, 7:10pm | 🎁 Bonus Rewarded | $1,000 Escalation Bonus Paid 🚀 |
💬 Team Correspondence & Comments:
🎯 jent-teleport (Dec 11, 11:59pm): "Thank you for the report @moaz219. I was able to reproduce this and agree with you that is a concerning privilege escalation in our new Access List functionality. I will let you know as soon as I have an update on this fix."
💰 Teleport Team (Dec 12, 9:33pm): "Thank you again for this and your other recent reports @moaz219!"
🎁 Teleport Team (Dec 20, 7:10pm): "Yes, I can confirm this report is eligible for the privilege escalation bonus. Thank you for asking!"
👤 Follow Me:
About the author
- AI Red Teamer & Bug Bounty Hunter | BSc in Computer Science | Recognized by: Google, Facebook, GitHub, Yandex, Quora, Oppo, Yelp, Teleport